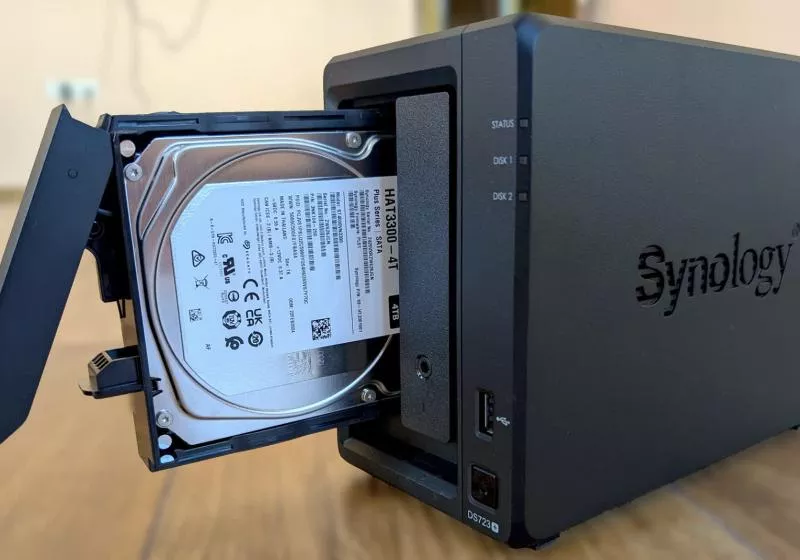
Synology patches a critical NAS flaw that could let attackers in without logging in
Posted
Via TechSpot
A newly published security advisory discloses two serious vulnerabilities in DiskStation Manager (DSM), the Linux-based OS used in Synology NAS products, one of them rated critical. The storage maker warned that the flaws could be abused to remotely access and attack vulnerable devices, giving cyber-criminals – or rogue AI agents,...